AWS Elastic Container Registry (ECR)
The ecr registry module lets you authenticate against private AWS Elastic Container Registry (ECR) repositories and monitor public images from public.ecr.aws.
Public images from public.ecr.aws work out of the box with zero configuration via the default ecr.public provider. AWS credentials are only required to authenticate against private ECR repositories.
⚙️ Configuration Variables
AWS IAM Access Key ID (required for private ECR registries)
AWS Account ID (used to filter when multiple accounts are configured)
Whether the registry is an ECR Public gallery. When set to true, AWS credentials are not required.
AWS Region Code (required for private ECR registries, defaults to us-east-1 when PUBLIC=true)
AWS IAM Secret Access Key (required for private ECR registries)
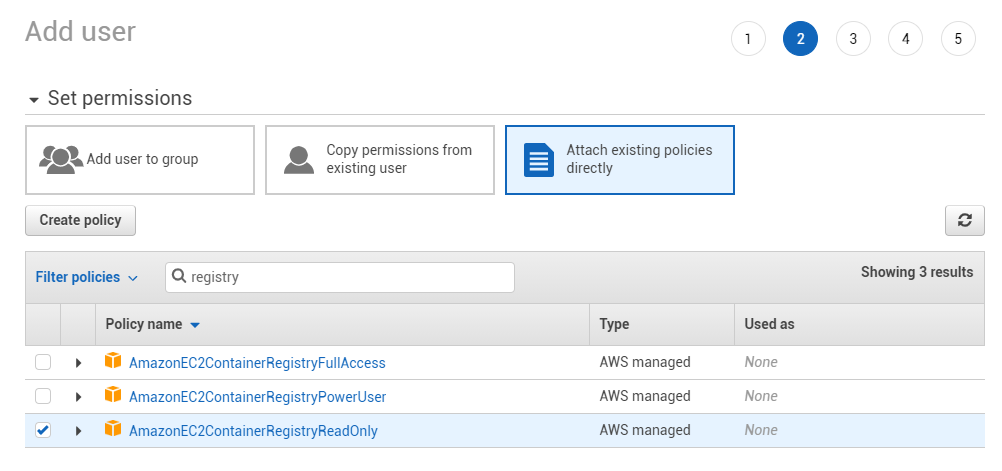
Ensure the AmazonEC2ContainerRegistryReadOnly policy (or equivalent ecr:GetAuthorizationToken, ecr:BatchGetImage, ecr:GetDownloadUrlForLayer permissions) is attached to the IAM user.
🚀 Examples
Monitor Public AWS ECR Images (public.ecr.aws)
Public images (for example public.ecr.aws/docker/library/traefik:latest) work automatically without any configuration.
Authenticate with Private AWS ECR
- Docker Compose
- Docker
services:
  whatsupdocker:
    image: getwud/wud
    environment:
      - WUD_REGISTRY_ECR_PRIVATE_ACCESSKEYID=AKIAIOSFODNN7EXAMPLE
      - WUD_REGISTRY_ECR_PRIVATE_SECRETACCESSKEY=wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY
      - WUD_REGISTRY_ECR_PRIVATE_REGION=eu-west-1
docker run \
  -e WUD_REGISTRY_ECR_PRIVATE_ACCESSKEYID="AKIAIOSFODNN7EXAMPLE" \
  -e WUD_REGISTRY_ECR_PRIVATE_SECRETACCESSKEY="wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY" \
  -e WUD_REGISTRY_ECR_PRIVATE_REGION="eu-west-1" \
  getwud/wud
📖 Setup Guide: Creating an AWS IAM User for ECR
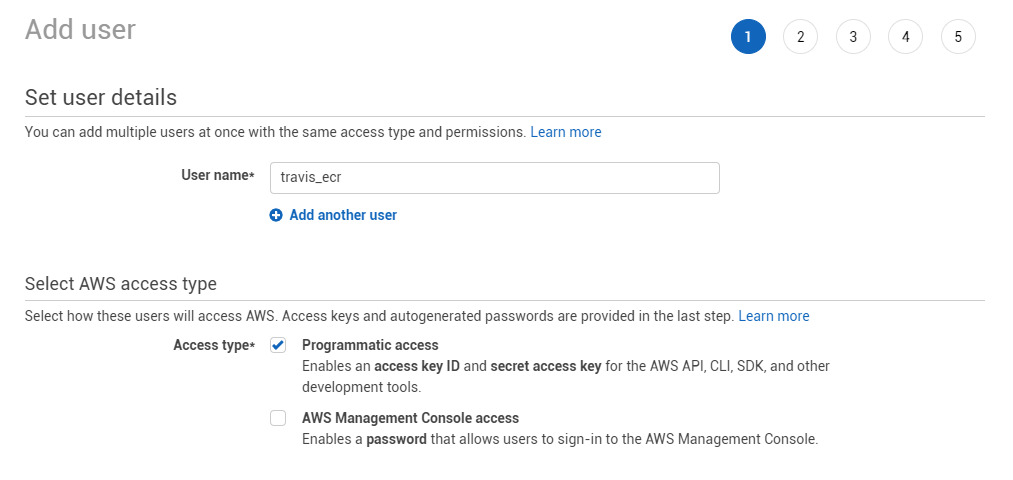
1. Create an IAM User
Open the AWS IAM Console and create a new IAM user.
2. Attach the Read-Only Policy
Attach the AmazonEC2ContainerRegistryReadOnly managed policy to the user.
3. Generate Access Keys
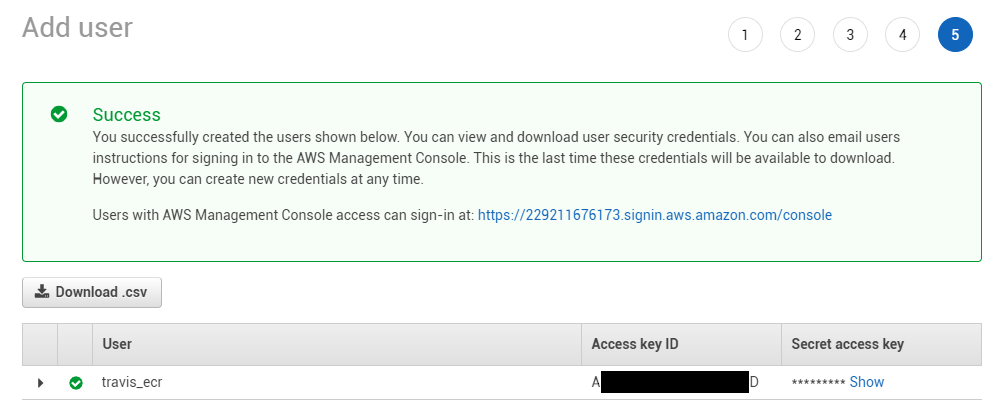
Create an Access Key under Security credentials, and copy the Access Key ID and Secret Access Key.